Cybersecurity
Cloakwave
Detect API security issues from your OpenAPI spec before code ships
A free API security scanner that analyzes OpenAPI specs and identifies vulnerabilities mapped to OWASP standards, running entirely in your browser.
Overview
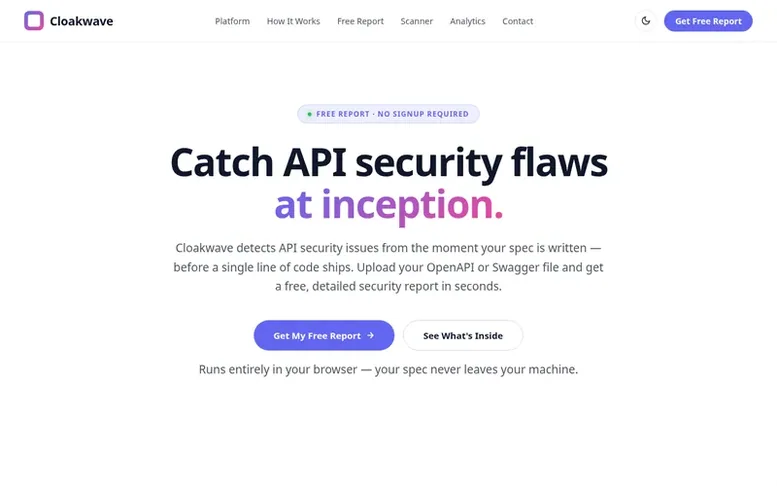
The Cloakwave homepage
Cloakwave detects API security issues at inception — the moment your specification is written — before any code is deployed. Upload your OpenAPI or Swagger file and receive a comprehensive security report within seconds.
The platform runs entirely in the browser, ensuring your spec never leaves your machine. It analyzes against 80+ security rules mapped to the OWASP API Top 10 and industry standards including PCI-DSS, SOC 2, HIPAA, and GDPR. Every finding includes what's wrong, why it matters, and specific remediation steps.
Beyond spec scanning, Cloakwave covers the full API lifecycle with AI Agent & MCP guardrails, OAuth & token security analysis, business logic vulnerability detection, compliance mapping, and shareable reports. Reports can be downloaded as HTML or shared via encoded URLs without server storage or account requirements.
Capabilities
- Inception Scan: Detect security issues in OpenAPI specs before code is written, covering auth gaps, mass assignment, PII exposure, and missing rate limits
- AI Agent & MCP Guardrails: Scan MCP server configs for tool poisoning, typosquatting, unpinned dependencies, and command injection
- OAuth & Token Security: Detect deprecated flows, missing PKCE, weak JWT algorithms, and missing token expiry
- Business Logic Analysis: Detect mass assignment risks, missing idempotency keys, and state-changing flows without rate control
- Compliance Mapping: Map findings to PCI-DSS, SOC 2, HIPAA, and GDPR controls for audit-ready evidence
- Shareable Reports: Download HTML reports or share links encoded in the URL without server storage
- 80+ security rules: Run against every spec and mapped to OWASP and industry standards
- Security scoring: 0–100 score with A–F grade for shareable assessment
- Prioritized findings: Sorted by severity (Critical, High, Medium, Low) with remediation steps
Pricing
Pricing model: Free
Follow Cloakwave to get an email when they post a milestone, ship a new product or add a demo video.
Cloakwave fact sheet
| Community votes | 0 |
|---|---|
| Website | cloakwave.io |
Cloakwave metrics
Vendor metrics for cloakwave.io: Ahrefs Domain Rating and Majestic link data, with the delta since the last review.
- Domain Rating
- 0
- no change since last check
- Trust Flow
- 0
- no change since last check
- Citation Flow
- 0
- no change since last check
- Referring domains
- 0
- no change since last check
- External backlinks
- 0
- no change since last check
Vendor Domain Rating (Ahrefs) checked 17 Nov 2026, spec changed 16 Nov 2026. Vendor Majestic data checked 16 Nov 2026, spec changed 16 Nov 2026. Link metrics supplied by Majestic. Trust Flow, Citation Flow and Topical Trust Flow are trademarks of Majestic-12 Ltd.
Cloakwave vendor domain
Open the vendor record
We read this from the registry's RDAP record on 16 Nov 2026, 16:50 UTC.
- Domain age
- 3 months
- Registered
- Expires
- Registrar
- NameCheap, Inc.
- DNSSEC
- Not signed
Cloakwave post-launch report
| Measure | At launch, then latest |
|---|---|
| Domain Rating (Ahrefs) | 0 first measured 16 Nov 2026 |
| Trust Flow (Majestic) | 0 first measured 16 Nov 2026 |
| Referring domains (Majestic) | 0 first measured 16 Nov 2026 |
Day 0 since launch. Next receipt: day 30, 16 Dec 2026. Many things move these figures, so a change is not proof of cause. Only stored readings are shown.
About to launch?
Plan your launch with our free playbook, from preparing your listing to choosing more launch directories.
- The week before
- On the day
- Week one
- Beyond launch
Buyer questions
Is my API spec uploaded to a server?
No. The scanner runs entirely in your browser. Your spec is parsed, analyzed, and scored locally — it is never uploaded, stored on a server, or transmitted anywhere. The only data that leaves your browser is the scan result saved to your own localStorage, and only if you scan more than once.
Is a finding a false positive?
The scanner uses deterministic rules against the OpenAPI spec, and some findings are heuristic — for example, a sequential ID pattern is flagged even if you enforce authorization elsewhere. If you report a false positive, include the finding title, the spec snippet that triggered it, and what the actual runtime behavior is.
Do you offer a paid plan?
Not yet. The scanner, breach-precedent report, and threat model are free. If you want features that require a backend — team dashboards, persistent scan history, scheduled scans, CI gating — email and describe what you need.
How do I report a vulnerability in Cloakwave itself?
Email info@cloakwave.io with reproduction steps. Please don't post it publicly or open a public issue. Receipt will be acknowledged within 48 hours and a fix and disclosure timeline coordinated from there.
Leave a review for Cloakwave
No customer reviews of Cloakwave yet. Write the first. Customer reviews are free and nobody can buy them.
Cloakwave has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
Compare with
| # | Product | DR | Votes |
|---|---|---|---|
| 1 |  WarditorFree security scan for vibe-coded apps built with AI tools |
1 +1 (up) since last check | 0 votes. Log in to vote for Warditor as a buyer |
| 2 |  ismycodesafe |
2 +1 (up) since last check | 0 votes. Log in to vote for ismycodesafe.com as a buyer |
| 3 |  Dep |
0 no change since last check | 0 votes. Log in to vote for DepRadar as a buyer |
| 4 |  tokenizenWe find the leaks. We publish the numbers. |
0 no change since last check | 0 votes. Log in to vote for tokenizen as a buyer |