Cybersecurity
DepRadar
Monitor direct and transitive dependencies for vulnerabilities across every repository
A dependency vulnerability monitoring platform that tracks direct and transitive dependencies across repositories with real-time alerts and dashboards, without
Overview
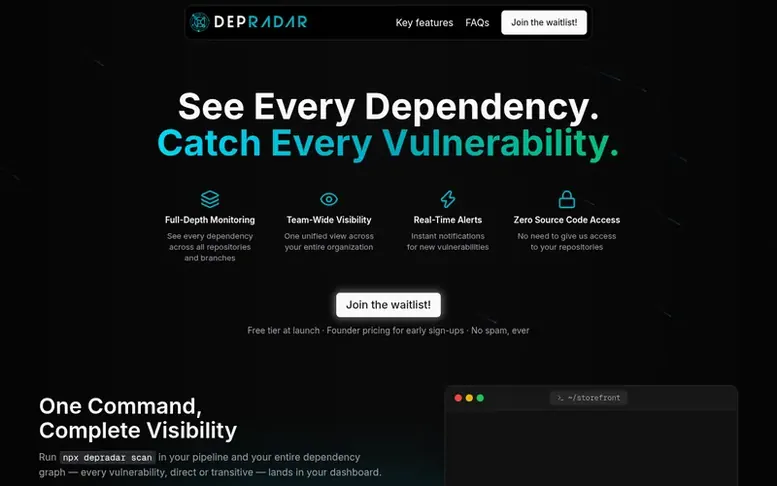
The DepRadar homepage
DepRadar monitors your complete dependency graph across all repositories to catch vulnerabilities in both direct and transitive dependencies. The platform provides real-time alerts when new vulnerabilities are published that affect your code, a centralized dashboard for viewing dependencies across multiple repositories and branches, and severity grading to help prioritize fixes.
The service respects code privacy by running an open-source CLI tool inside your CI/CD pipeline that transmits only dependency metadata—never your source code. DepRadar integrates with any CI/CD tool including GitHub Actions, GitLab, Bitbucket, and Azure DevOps with a single command. Every snapshot captured is already a complete inventory of your software supply chain, with SBOM exports in industry-standard formats planned for after the initial beta release.
Capabilities
- Full-depth dependency graph monitoring for direct and transitive dependencies
- Real-time vulnerability alerts via dashboard, email and Slack
- Severity grading to prioritize vulnerability fixes
- Centralized multi-repository and multi-branch dashboard
- Open-source CLI tool with zero source code access
- CI/CD integration with GitHub Actions, GitLab, Bitbucket and Azure DevOps
- Complete software supply chain inventory snapshots
- Exact dependency paths showing how vulnerabilities enter your code
- Continuous monitoring with new vulnerability advisory updates
- Planned SBOM export in CycloneDX and SPDX formats
Pricing
Pricing model: Freemium
Free tier at launch with founder pricing for early sign-ups
Follow DepRadar to get an email when they post a milestone, ship a new product or add a demo video.
DepRadar fact sheet
| Community votes | 0 |
|---|---|
| Stage | MVP |
| Website | depradar.dev |
DepRadar metrics
Vendor metrics for depradar.dev: Ahrefs Domain Rating and Majestic link data, with the delta since the last review.
- Domain Rating
- 0
- no change since last check
- Trust Flow
- 0
- no change since last check
- Citation Flow
- 0
- no change since last check
- Referring domains
- 0
- no change since last check
- External backlinks
- 0
- no change since last check
Vendor Domain Rating (Ahrefs) checked 6 Nov 2026, spec changed 3 Nov 2026. Vendor Majestic data checked 3 Nov 2026, spec changed 3 Nov 2026. Link metrics supplied by Majestic. Trust Flow, Citation Flow and Topical Trust Flow are trademarks of Majestic-12 Ltd.
DepRadar vendor domain
Open the vendor record
We read this from the registry's RDAP record on 6 Nov 2026, 04:02 UTC.
- Domain age
- 1 year
- Registered
- Expires
- Registrar
- CloudFlare, Inc.
- DNSSEC
- Not signed
DepRadar post-launch report
| Measure | At launch, then latest |
|---|---|
| Domain Rating (Ahrefs) | 0 to 0 no change since launch 3 Nov 2026, then 6 Nov 2026 |
| Trust Flow (Majestic) | 0 first measured 3 Nov 2026 |
| Referring domains (Majestic) | 0 first measured 3 Nov 2026 |
Day 2 since launch. Next receipt: day 30, 3 Dec 2026. Many things move these figures, so a change is not proof of cause. Only stored readings are shown.
About to launch?
Plan your launch with our free playbook, from preparing your listing to choosing more launch directories.
- The week before
- On the day
- Week one
- Beyond launch
Compare and explore
See the alternatives to DepRadar, Bottyfier vs DepRadar, Binarly vs DepRadar, StarCheck vs DepRadar, Kloudle vs DepRadar, FraudNova vs DepRadar, tokenizen vs DepRadar, more in Cybersecurity.
Buyer questions
What data does DepRadar collect?
DepRadar is designed to collect and store only dependency information. Your code never leaves your CI—only the dependency graph is sent to DepRadar. The CLI tool is open-source so anyone can verify exactly what data is being transmitted.
Does DepRadar detect vulnerabilities in transitive dependencies?
Yes. Most known vulnerabilities enter a project through indirect transitive dependencies that direct dependency checks miss entirely. DepRadar captures your full resolved dependency graph, so every package is matched against known vulnerabilities, and shows the exact dependency path for each vulnerable package.
What types of dependencies does DepRadar support at launch?
DepRadar is focusing on JavaScript at launch and will support anything with a package.json file for the initial release. Support for other languages including Python, Rust and Ruby is planned, and the open-source CLI and well-documented APIs will allow custom connectors for any language or framework.
Can DepRadar generate an SBOM?
Every DepRadar snapshot is already a complete, versioned inventory of your software supply chain that can be viewed and explored through dashboards. One-click SBOM exports in industry-standard formats such as CycloneDX and SPDX are on the roadmap, planned for shortly after the initial beta release.
Can DepRadar generate an SBOM (Software Bill of Materials)?
Under the hood, every DepRadar snapshot is already a complete, versioned inventory of your software supply chain — exactly the data an SBOM is made of. From day one you can view and explore all of it through your dashboards. One-click SBOM exports in industry-standard formats such as CycloneDX and SPDX are on our roadmap, planned for shortly after our initial beta release.
Leave a review for DepRadar
No customer reviews of DepRadar yet. Write the first. Customer reviews are free and nobody can buy them.
DepRadar has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
Compare with
| # | Product | DR | Votes |
|---|---|---|---|
| 1 |  tokenizenWe find the leaks. We publish the numbers. |
0 no change since last check | 0 votes. Log in to vote for tokenizen as a buyer |
| 2 |  Fraud |
0 no change since last check | 0 votes. Log in to vote for FraudNova as a buyer |
| 3 |  Korzen Bot ProtectionCustomers in, bots out |
0 no change since last check | 0 votes. Log in to vote for Korzen Bot Protection as a buyer |
| 4 |  fail2zigLog-based intrusion prevention for Linux that detects repeated authentication failures and bans offending IP addresses with kernel-enforced protection. |
0 no change since last check | 0 votes. Log in to vote for fail2zig as a buyer |