DevOps & CI/CD
Preflyt
Pre-deployment security scanner for web apps, APIs, and backends
Detects exposed secrets, open ports, and misconfigurations in live web deployments in under 30 seconds, with no signup required.
Overview
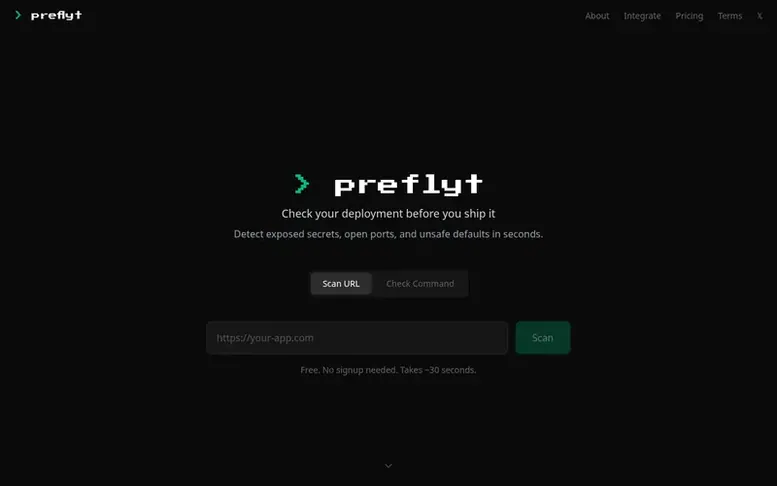
The Preflyt homepage
Preflyt is a post-deployment exposure scanner that analyzes live web applications, APIs, and backends for security issues without requiring signup or installation. It checks for exposed configuration files, git repositories, backup files, open database ports, and missing security headers in under 30 seconds.
All checks are read-only and non-intrusive, with no modifications to your systems. Preflyt can be run via a web interface, integrated into CI/CD pipelines with a command-line tool, or used by AI coding agents. It differs from source code scanners like Snyk by focusing on deployment-time issues that only become visible once an application is running on a server.
The service offers a free tier with 3 scans and a Pro plan for unlimited scanning. Reports are shareable and expire after 30 days.
Capabilities
- Exposed .env and config file detection
- Open database port scanning
- Security header analysis
- CORS misconfiguration detection
- Cookie security analysis
- Git repository exposure detection
- Backup file exposure detection
- Source map exposure detection
- Terminal command security checker
- CDN-aware scanning
Pricing
Pricing model: Freemium
Free: $0 with 3 security scans, command checker (unlimited), AI fix prompts, no signup required. Pro: $9.99/month with unlimited security scans, priority scans, everything in Free, and priority support.
Follow Preflyt to get an email when they post a milestone, ship a new product or add a demo video.
Preflyt fact sheet
| Community votes | 0 |
|---|---|
| Website | preflyt.dev |
Preflyt metrics
Vendor metrics for preflyt.dev: Ahrefs Domain Rating and Majestic link data, with the delta since the last review.
- Domain Rating
- 3
- no change since last check
- Trust Flow
- 10
- no change since last check
- Citation Flow
- 18
- no change since last check
- Referring domains
- 54
- no change since last check
- External backlinks
- 73
- no change since last check
Vendor Domain Rating (Ahrefs) checked 6 Nov 2026, spec changed 18 Oct 2026. Vendor topic: Sports/Martial Arts (10). Vendor Majestic data checked 18 Oct 2026, spec changed 18 Oct 2026. Link metrics supplied by Majestic. Trust Flow, Citation Flow and Topical Trust Flow are trademarks of Majestic-12 Ltd.
Preflyt vendor domain
Open the vendor record
We read this from the registry's RDAP record on 6 Nov 2026, 06:22 UTC.
- Domain age
- 8 months
- Registered
- Expires
- Registrar
- CloudFlare, Inc.
- DNSSEC
- Not signed
Preflyt post-launch report
| Measure | At launch, then latest |
|---|---|
| Domain Rating (Ahrefs) | 3 to 3 no change since launch 18 Oct 2026, then 5 Nov 2026 |
| Trust Flow (Majestic) | 10 first measured 18 Oct 2026 |
| Referring domains (Majestic) | 54 first measured 18 Oct 2026 |
Day 19 since launch. Next receipt: day 30, 17 Nov 2026. Many things move these figures, so a change is not proof of cause. Only stored readings are shown.
About to launch?
Plan your launch with our free playbook, from preparing your listing to choosing more launch directories.
- The week before
- On the day
- Week one
- Beyond launch
Compare and explore
See the alternatives to Preflyt, Preflyt vs RepoFlow, Crontinel vs Preflyt, CloudPloy vs Preflyt, Preflyt vs ArthaOps, Preflyt vs Termal OS, Preflyt vs Omynix, more in DevOps & CI/CD.
Buyer questions
What is Preflyt?
Preflyt is a free pre-deployment security scanner that checks live web applications for exposed secrets, misconfigurations, and unsafe defaults in under 30 seconds without requiring signup.
How does Preflyt detect exposed .env files?
Preflyt makes HTTP requests to common .env file paths on your live server and checks if they return sensitive configuration data like database passwords, API keys, or secret tokens.
Does Preflyt scan open ports?
Yes, Preflyt scans 18 commonly exposed ports including MySQL (3306), PostgreSQL (5432), MongoDB (27017), Redis (6379), and development servers, with CDN detection to avoid false positives.
Is Preflyt safe to use on my website?
Yes, Preflyt only performs non-intrusive, read-only checks and does not attempt to exploit vulnerabilities, modify data, or perform any destructive actions.
How is Preflyt different from Snyk or other vulnerability scanners?
Snyk analyzes source code and dependencies for known CVEs, while Preflyt scans your live deployment from outside to find exposed files, open ports, and misconfigurations that only exist once your app is running on a server.
Leave a review for Preflyt
No customer reviews of Preflyt yet. Write the first. Customer reviews are free and nobody can buy them.
Preflyt has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
Compare with
| # | Product | DR | Votes |
|---|---|---|---|
| 1 |  Flowrensic™Forensics for durable execution |
2 +1 (up) since last check | 0 votes. Log in to vote for Flowrensic™ as a buyer |
| 2 |  BuildkiteProgrammable CI orchestration for AI |
76 no change since last check | 0 votes. Log in to vote for Buildkite as a buyer |
| 3 |  Queue |
0 no change since last check | 0 votes. Log in to vote for QueueForge as a buyer |
| 4 |  CDvizOpen-source CI/CD observability platform for monitoring software delivery pipelines |
10 no change since last check | 0 votes. Log in to vote for CDviz as a buyer |