Cybersecurity
fail2zig
Log-based intrusion prevention for Linux that detects repeated authentication failures and bans offending IP addresses with kernel-enforced protection.
Log-based intrusion prevention for Linux that detects repeated authentication failures and bans offending IP addresses with kernel-enforced protection.
Overview
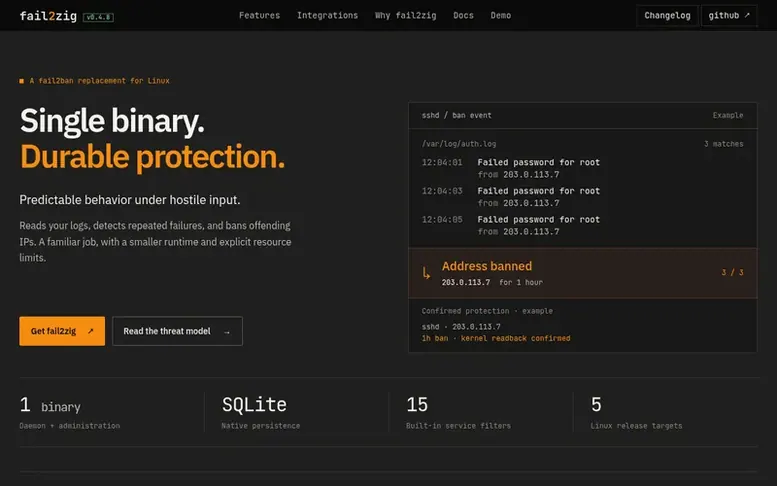
The fail2zig homepage
fail2zig is a fail2ban replacement for Linux that provides log-based intrusion prevention. It reads service logs to detect repeated authentication failures and scan events, then enforces kernel-level bans against offending IP addresses using nftables, iptables, or ipset.
The tool ships as a single static binary combining the daemon, administration tools, and migration utilities. It uses SQLite for durable protection state that survives restarts, with explicit resource limits to prevent resource exhaustion. Built-in filters recognize common failure patterns for SSH, web probes, and mail services without requiring a regex engine.
fail2zig supports migration from fail2ban configurations, allowing users to import existing jails, review compatibility, and verify behavior before switching. Protection policies are configurable per jail with customizable retry thresholds, observation windows, ban durations, and escalation rules for repeat offenders.
Capabilities
- Single static binary deployment
- SQLite-based durable state
- Kernel-enforced firewall rules via nftables, iptables or ipset
- Built-in service filters for sshd, web and mail services
- Configurable jail policies with thresholds and escalation
- fail2ban configuration migration support
- Bounded resource limits and memory controls
- Firewall rule inspection and verification
- IPv4 and IPv6 protection
- Threat model documentation
Follow fail2zig to get an email when they post a milestone, ship a new product or add a demo video.
fail2zig fact sheet
| Community votes | 0 |
|---|---|
| Based in | United States |
| Website | fail2zig.com |
fail2zig metrics
Vendor metrics for fail2zig.com: Ahrefs Domain Rating and Majestic link data, with the delta since the last review.
- Domain Rating
- 0
- no change since last check
- Trust Flow
- 0
- no change since last check
- Citation Flow
- 10
- no change since last check
- Referring domains
- 21
- no change since last check
- External backlinks
- 117
- no change since last check
Vendor Domain Rating (Ahrefs) checked 6 Nov 2026, spec changed 1 Nov 2026. Vendor Majestic data checked 1 Nov 2026, spec changed 1 Nov 2026. Link metrics supplied by Majestic. Trust Flow, Citation Flow and Topical Trust Flow are trademarks of Majestic-12 Ltd.
fail2zig vendor domain
Open the vendor record
We read this from the registry's RDAP record on 5 Nov 2026, 18:38 UTC.
- Domain age
- 6 months
- Registered
- Expires
- Registrar
- Cloudflare, Inc.
- DNSSEC
- Not signed
fail2zig post-launch report
| Measure | At launch, then latest |
|---|---|
| Domain Rating (Ahrefs) | 0 to 0 no change since launch 1 Nov 2026, then 5 Nov 2026 |
| Trust Flow (Majestic) | 0 first measured 1 Nov 2026 |
| Referring domains (Majestic) | 21 first measured 1 Nov 2026 |
Day 4 since launch. Next receipt: day 30, 1 Dec 2026. Many things move these figures, so a change is not proof of cause. Only stored readings are shown.
About to launch?
Plan your launch with our free playbook, from preparing your listing to choosing more launch directories.
- The week before
- On the day
- Week one
- Beyond launch
Compare and explore
See the alternatives to fail2zig, more in Cybersecurity or startups in United States.
Buyer questions
Is fail2zig a drop-in replacement for fail2ban?
No. Users must inspect supported configuration and action scope before switching. The migration workflow can transfer jail owners, deadlines and history, but not partial regex matches or journal cursors. Arbitrary fail2ban regexes and shell actions are not executed.
Can hostile log lines crash or exhaust the daemon?
The threat model was designed to prevent this. Parsing is bounds-checked, log lines have bounded input limits, and native processing has explicit resource limits. Storage failures pause affected ingestion while retaining protection, reducing risk.
Why was fail2zig written in Zig instead of Rust?
Zig provides explicit allocator control, comptime code generation for built-in filters, and straightforward cross-compilation to musl targets. The developers note that Rust would work, but Zig fits the problem better.
Does fail2zig run in minimal containers?
Static linkage avoids shared runtime dependencies, but deployment still requires readable logs, writable persistent state, and the selected firewall backend's capabilities. Journal input needs journalctl; iptables/ipset need host tools. Effects stay in the current network namespace; custom namespace selectors are unsupported.
Is fail2zig a SIEM or a WAF?
Neither. fail2zig reads logs and acts on repeated failures. It does not aggregate security events across hosts, correlate incidents, or inspect HTTP bodies.
Leave a review for fail2zig
No customer reviews of fail2zig yet. Write the first. Customer reviews are free and nobody can buy them.
fail2zig has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
Compare with
| # | Product | DR | Votes |
|---|---|---|---|
| 1 |  Dep |
0 no change since last check | 0 votes. Log in to vote for DepRadar as a buyer |
| 2 |  tokenizenWe find the leaks. We publish the numbers. |
0 no change since last check | 0 votes. Log in to vote for tokenizen as a buyer |
| 3 |  Fraud |
0 no change since last check | 0 votes. Log in to vote for FraudNova as a buyer |
| 4 |  Korzen Bot ProtectionCustomers in, bots out |
0 no change since last check | 0 votes. Log in to vote for Korzen Bot Protection as a buyer |